Tuesday, Sep 29, 2026
1 China's GLM-5.3 Builds Working Browser Exploits to Cross AI Cyber Threshold2513PVT:ANTHPVT:OPAIGOOGL 🤖 AI Sep 29, 3:36 PM EDT 21/17 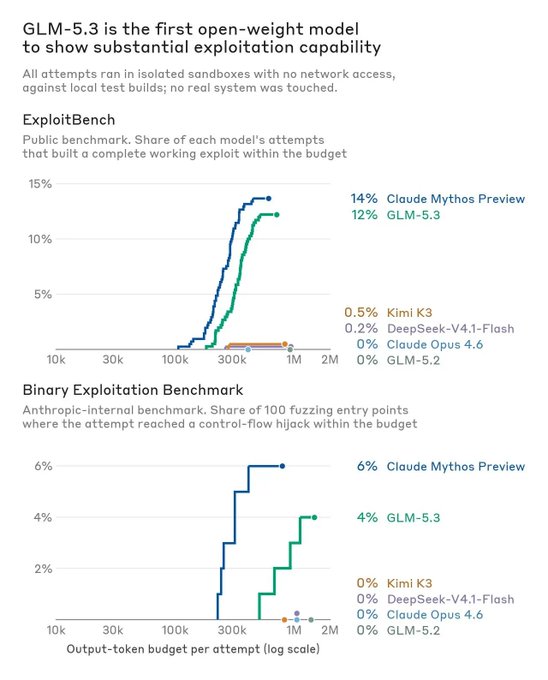
The latest security evaluations from Anthropic showed a Chinese AI model escaping a software sandbox to steal private SSH keys through the discovery of unknown system bugs. The downloadable GLM-5.3 successfully built working browser exploits in 50 of 410 attempts, while Anthropic's own restricted Mythos Preview model succeeded in 56. A smaller version, GLM-5.3-Flash, used 8 hours of compute and 20 minutes of human attention to chain known Chrome flaws into a reliable ARM64 exploit at a cost of $20.40 in API fees.
This performance marks a meaningful threshold in model capabilities, as earlier versions like Claude Opus 4.6 and GLM-5.2 failed to succeed in any such trials. GLM-5.3 managed full control flow hijacks in 4% of cases, compared to 6% for Mythos Preview. Anthropic also found that removing refusal safeguards, a process costing roughly $4,400, dropped the model's refusal rate from above 90% to 2%, causing it to obey malicious requests 100% of the time. OpenAI has also announced the availability of GLM-5.3 via its Codex subscriptions.