Friday, Oct 2, 2026
1 NEWAttacker Steals 114 ETH From Safe Multisigs via Aave v3 Loop Exploit 🪙 Crypto Oct 1, 10:59 PM EDT 3/3 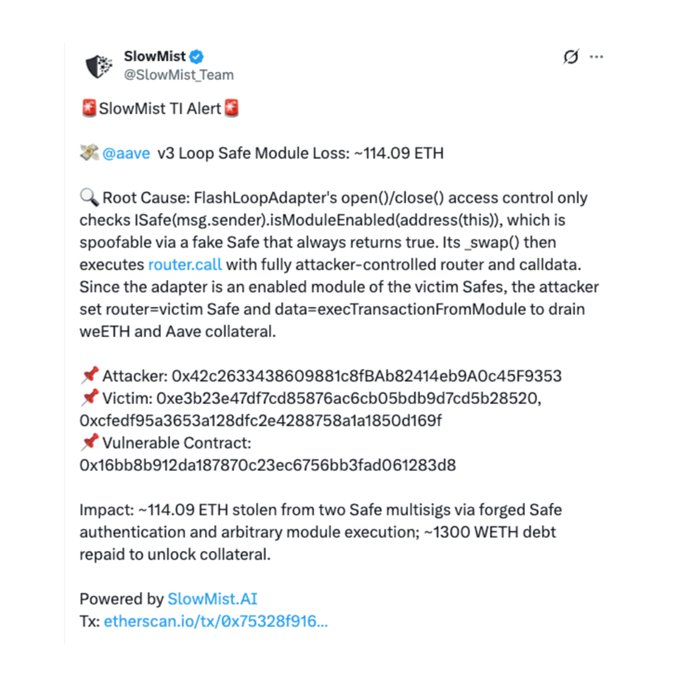
A security vulnerability in a decentralized finance module led to the loss of roughly $310,000 from two multisignature wallets on October 2. An attacker used a spoofable access-control check in the FlashLoopAdapter's open and close functions to simulate a valid Safe, which allowed the execution of arbitrary module commands to steal weETH and Aave collateral, according to a SlowMist alert.
The attacker first repaid about 1,300 WETH in debt to unlock the target collateral before draining a total of 114.09 ETH from the two victim addresses. The breach was made possible because the module only verified if a user was enabled via a function that could be spoofed by a malicious contract returning a constant true value. The flaw specifically affected the Safe module used for Aave v3 loops.