Thursday, Oct 1, 2026
1 Mandiant Traces $387.5M Bitget Hack From Security Appliances to Wallet Server 🪙 Crypto Sep 24, 5:38 PM EDT 238/54 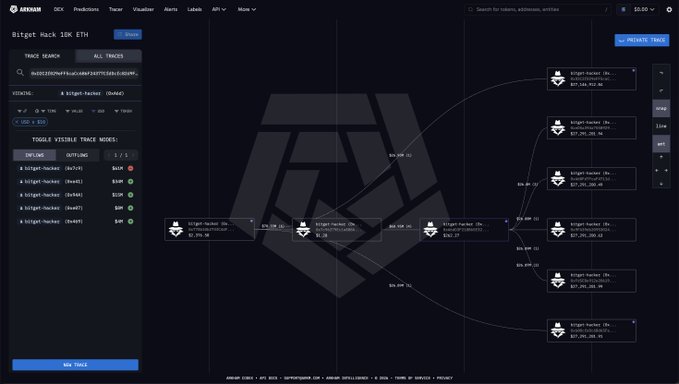
Mandiant found that attackers behind Bitget’s $387.5 million theft moved from compromised security appliances into the crypto exchange’s wallet environment and installed malicious packages on its wallet job server. The intruders gained access by exploiting a zero-day vulnerability in a third-party security product before draining funds on Sept. 24.
SlowMist’s investigation traced malicious activity tied to the breach back to Aug. 31 and recovered a customized tool designed to interact with the wallet system’s withdrawal logic. It also identified unauthorized access to a security product’s management platform using an internal employee identity. Bitget CEO Gracy Chen has said stolen internal credentials allowed attackers to issue fraudulent withdrawal commands and bypass risk controls without compromising wallet private keys.
Security researcher Tayvano attributed the attack to North Korea, saying, "These are the same attackers as Bybit, AFX, LayerZero, KelpDAO ... It's North Korea." Bitget has begun restoring withdrawals in phases and replenished its user protection fund to more than $300 million on Sept. 30. The exchange has said customers will be fully covered regardless of whether the stolen funds are recovered.