Saturday, Sep 19, 2026
1 FomoPeek App Versions 1.1 to 1.2 Steal Crypto Keys Using Root iOS ExploitAAPL 🔒 Cybersecurity Sep 19, 7:08 AM EDT 3/3 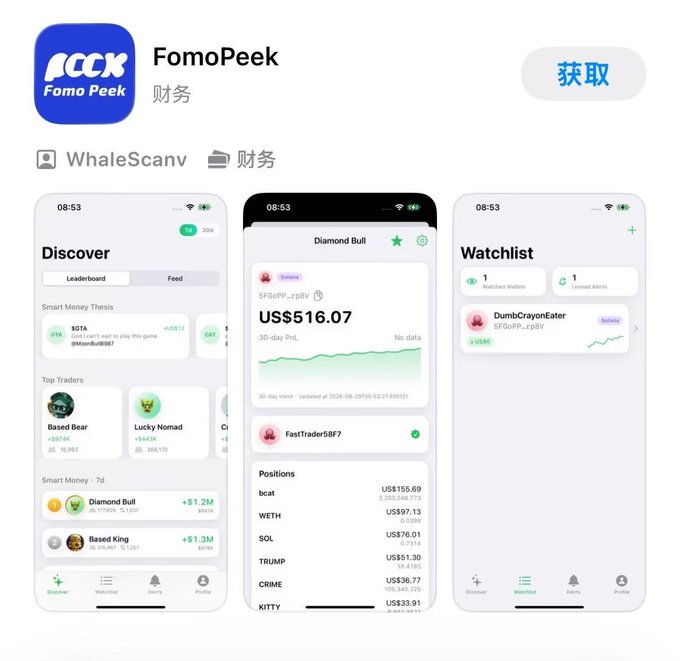
Security firm SlowMist and exchange OKX warned that the FomoPeek "smart money" tracking application contains a malicious iOS kernel attack framework. Versions 1.1 to 1.2 of the app integrate 8 vulnerability exploit schemes that automatically select an attack path based on the device model and system version to steal private keys and mnemonic seed phrases. The malware enables hackers to gain root privileges and access sensitive data stored across all applications on the affected iPhone or iPad, prompting Binance to issue a broad security advisory.
The attack targets iOS versions 13 through 26.5 by luring users to malicious webpages via Safari to trigger memory corruption in WebKit or JavaScriptCore. The process bypasses Pointer Authentication Codes, escapes the WebContent sandbox, and completes kernel privilege escalation to drain device Keychains and local crypto wallet data. Affected users are advised to delete the app, update their operating system, and transfer funds to new wallets created on clean devices.