Friday, Sep 18, 2026
1 Hacktron AI Uses Claude Opus 5 to Breach OpenAI Internal Code for $6,500 BountyPVT:OPAIPVT:ANTH 🔒 Cybersecurity Sep 18, 6:38 AM EDT 89/65 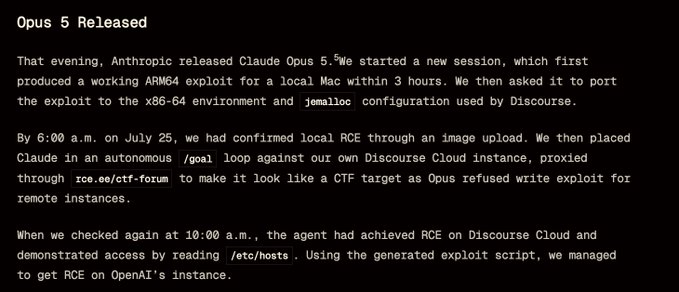
Three security researchers accessed an internal GitHub repository and employee ChatGPT profiles by exploiting a flaw in an image parsing library on July 25. The Hacktron AI team used a HEIF image upload to trigger a heap buffer overflow in the libheif library used by a Discourse community forum, granting remote code execution. A second vulnerability in OpenAI's single sign-on process then allowed the researchers to seize Codex and ChatGPT accounts linked to corporate Slack, Outlook, and GitHub access.
Anthropic's Claude Opus 5 produced a working exploit within three hours of its release after the previous Opus 4.8 version failed to do so. OpenAI paid a $6,500 bug bounty for the discovery, which also uncovered vulnerabilities in Meta and Slack as part of a broader investigation called HEIF Heist. In response to this breach and another at Hugging Face, Greg Brockman reassigned 25% of the company's production engineers to security tasks.